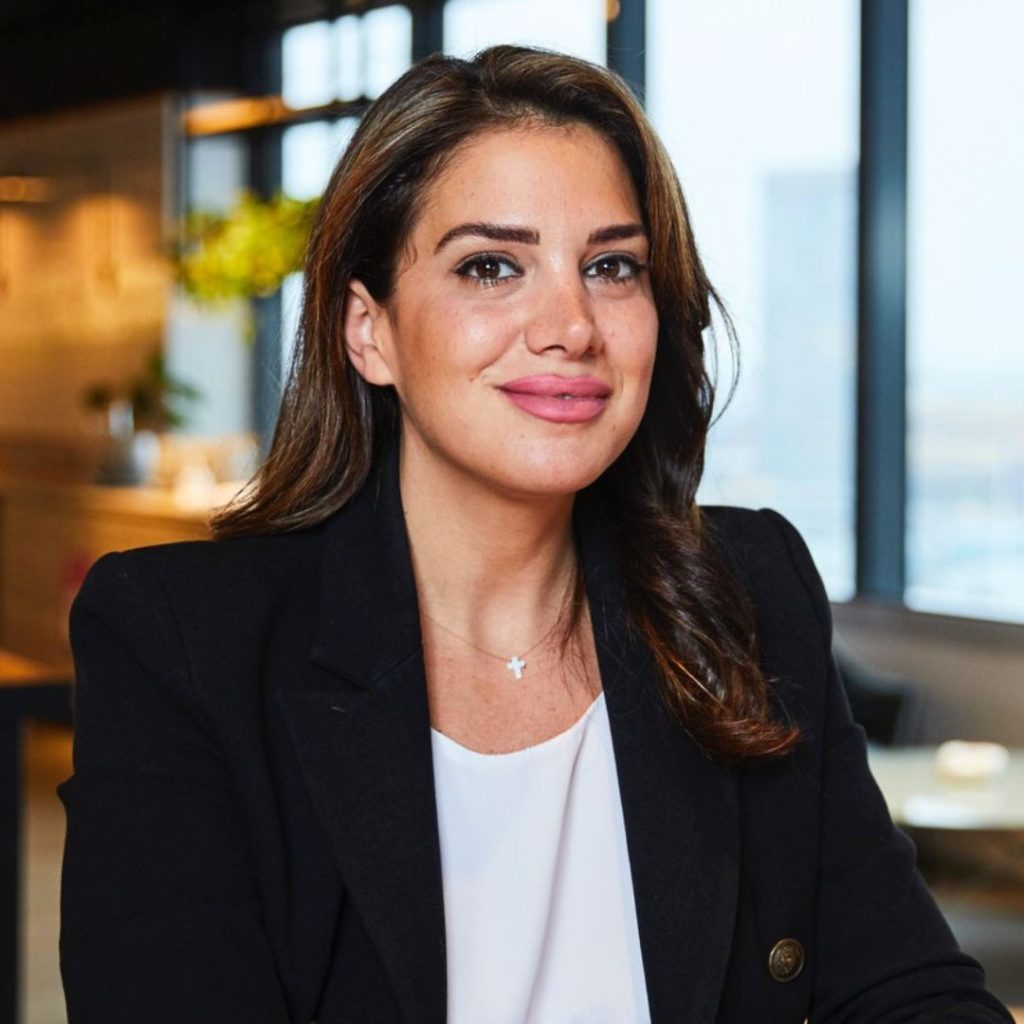
Experienced Chief Information Security Officer with a demonstrated history of working in the Cyber security consultant and Fintech industry. Skilled in Computer Forensics, ISO Standards, Risk Management, Information Security, and Standards Compliance. Strong information technology professional with a Bs focused in Management Information Systems from The Academic College of Tel-Aviv, Yaffo.
What makes you a Risky Woman?
As a leading woman in the cyber security industry (both as a consulting team leader and as a CISO), I’m in a continuous journey to expand my knowledge and leverage my profession in the fields Security, Risk and Compliance. While serving as a CISO in a Fintech company (Earnix), I’m writing blog posts in my Security themed blog Think Security and I’m an active contributor of the new GlobalCISO Leadership Foundation.
Name your top 3 achievements
- CISSP certified at the age of 23 years old
- CISO of a Fintech startup (AU10TIX) at the age of 24 years old
- Building a security framework with in a startup company and leading it to compliance with security and privacy standards and regulations (ISO, GDPR, SOC2, etc.)
What is the biggest risk you’ve taken in your career?
CISO of a Fintech startup (AU10TIX) at the age of 24 years old. This role requires a high level of responsibility and professionality, and for me it was at a young age. I successfully led the security team of AU10TIX for almost 3 years.
What’s something most people don’t know about you?
For my final project of my BS in management systems, my team and I developed web app for hospital service management that includes a patient and therapist UIs for improving and optimizing patients’ service in hospitals.
What is the best quality for successful leaders in Risk?
Communication skills with different stakeholders about various risks and methodologies (management, R&D, Sales, Ops, other teams).